PRIVATE NETWORK
Secure communication
between your services,
on one cloud or across
several.
Your services talk to each other encrypted and by name, wherever they run. Split your app across clouds without opening ports or managing VPNs.
Start now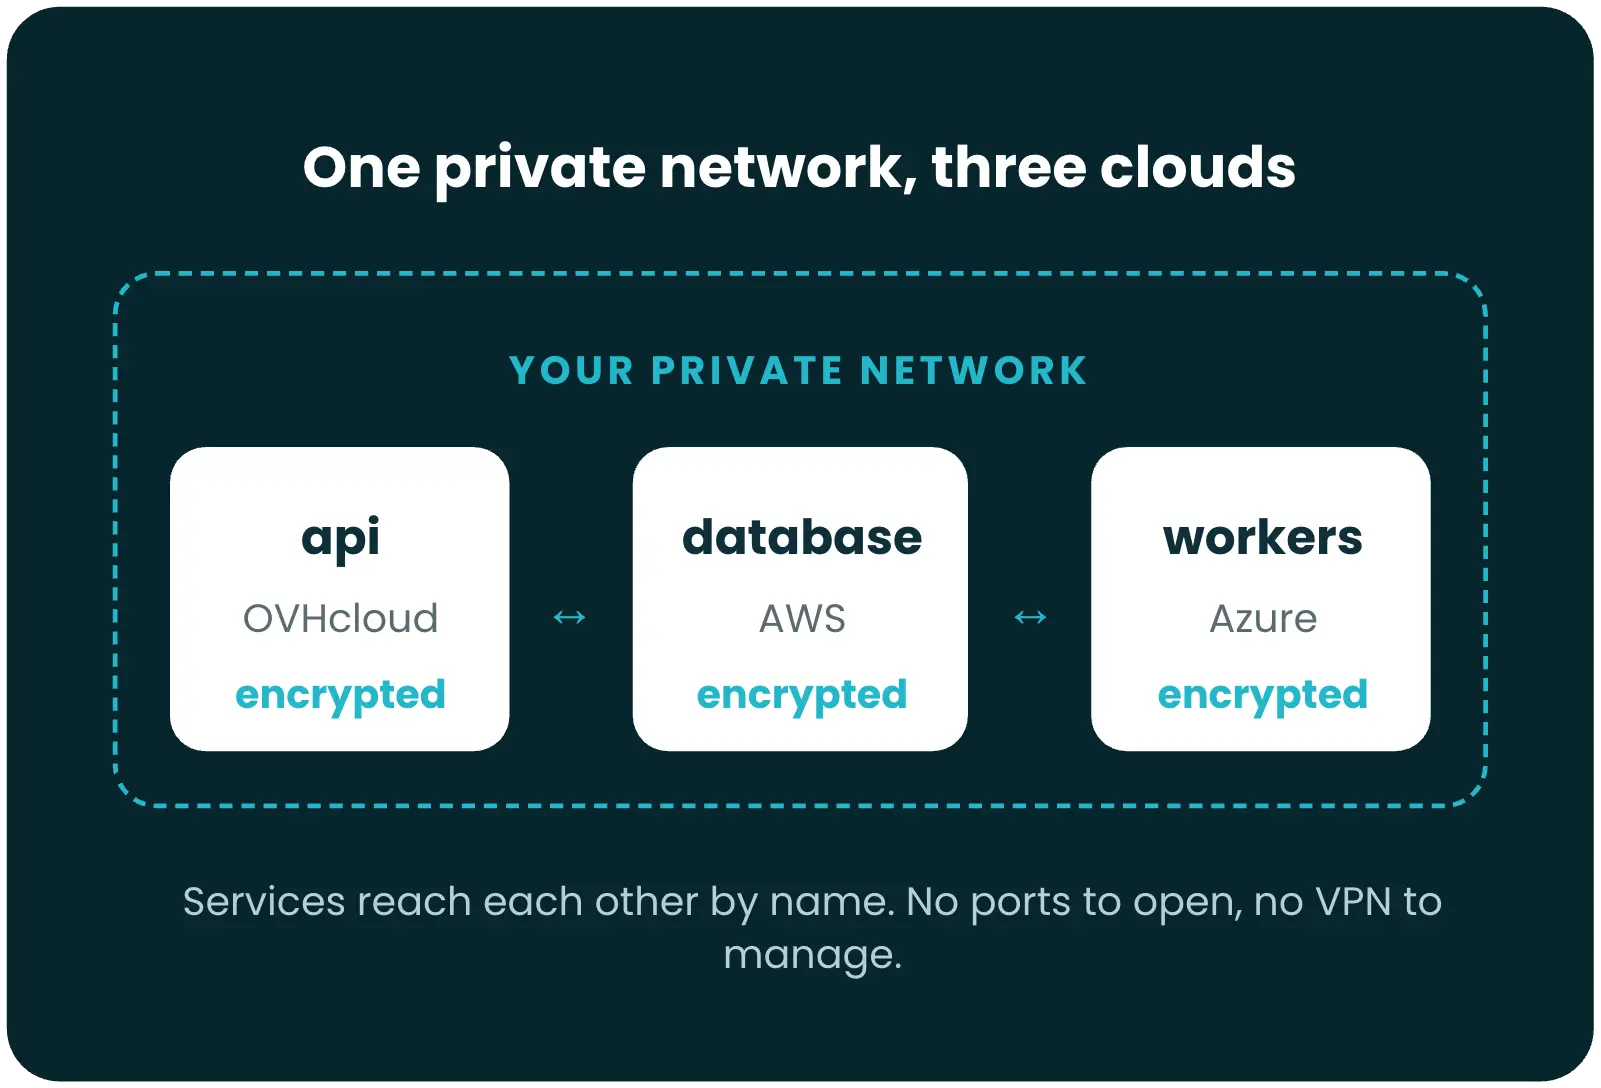
We want to split services across clouds,
but exposing internal traffic worries us.
Running each part of your app where it makes sense is the easy decision. Connecting those parts is where it gets uncomfortable: public endpoints, firewall rules, VPN tunnels and secrets that travel further than they should. Axebow puts every service on the same private network, whatever cloud it runs on, and takes care of connecting them.
Connected. Encrypted. Anywhere.
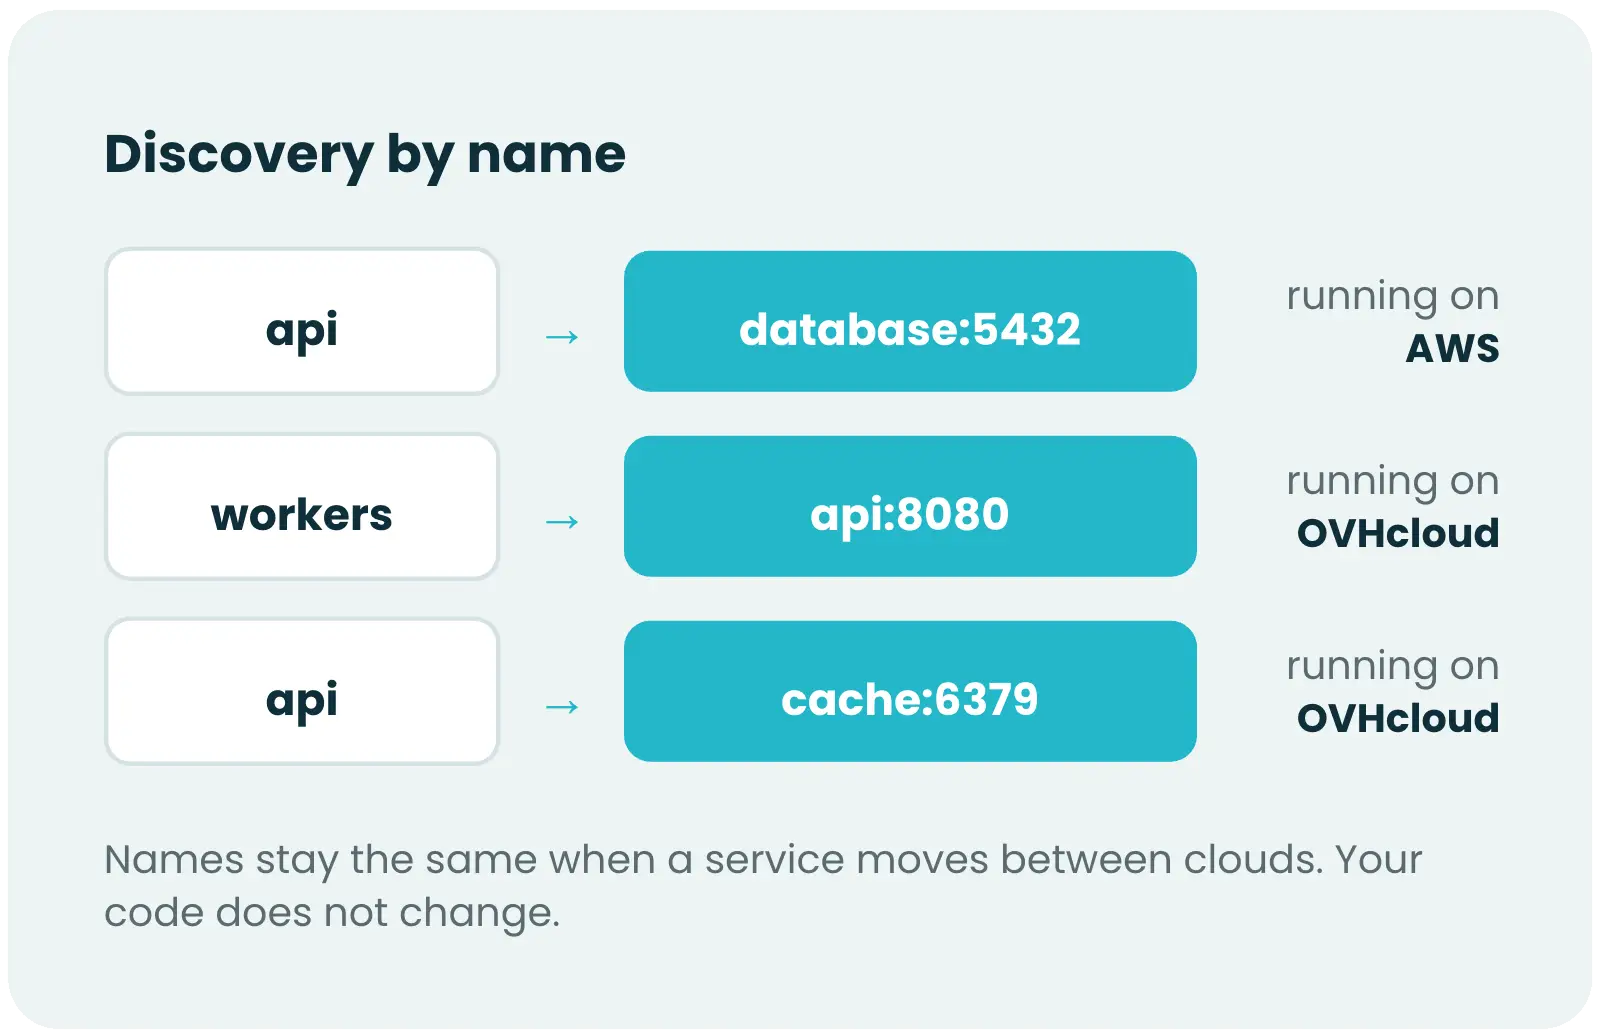
Services find each other by name
Each service in your deployment gets a name. Any other service reaches it with that name, the same way it would on a single machine. No IP lists to keep up to date, no load balancer to configure, no addresses that change when a cloud moves a node.
Encrypted traffic, nothing to expose
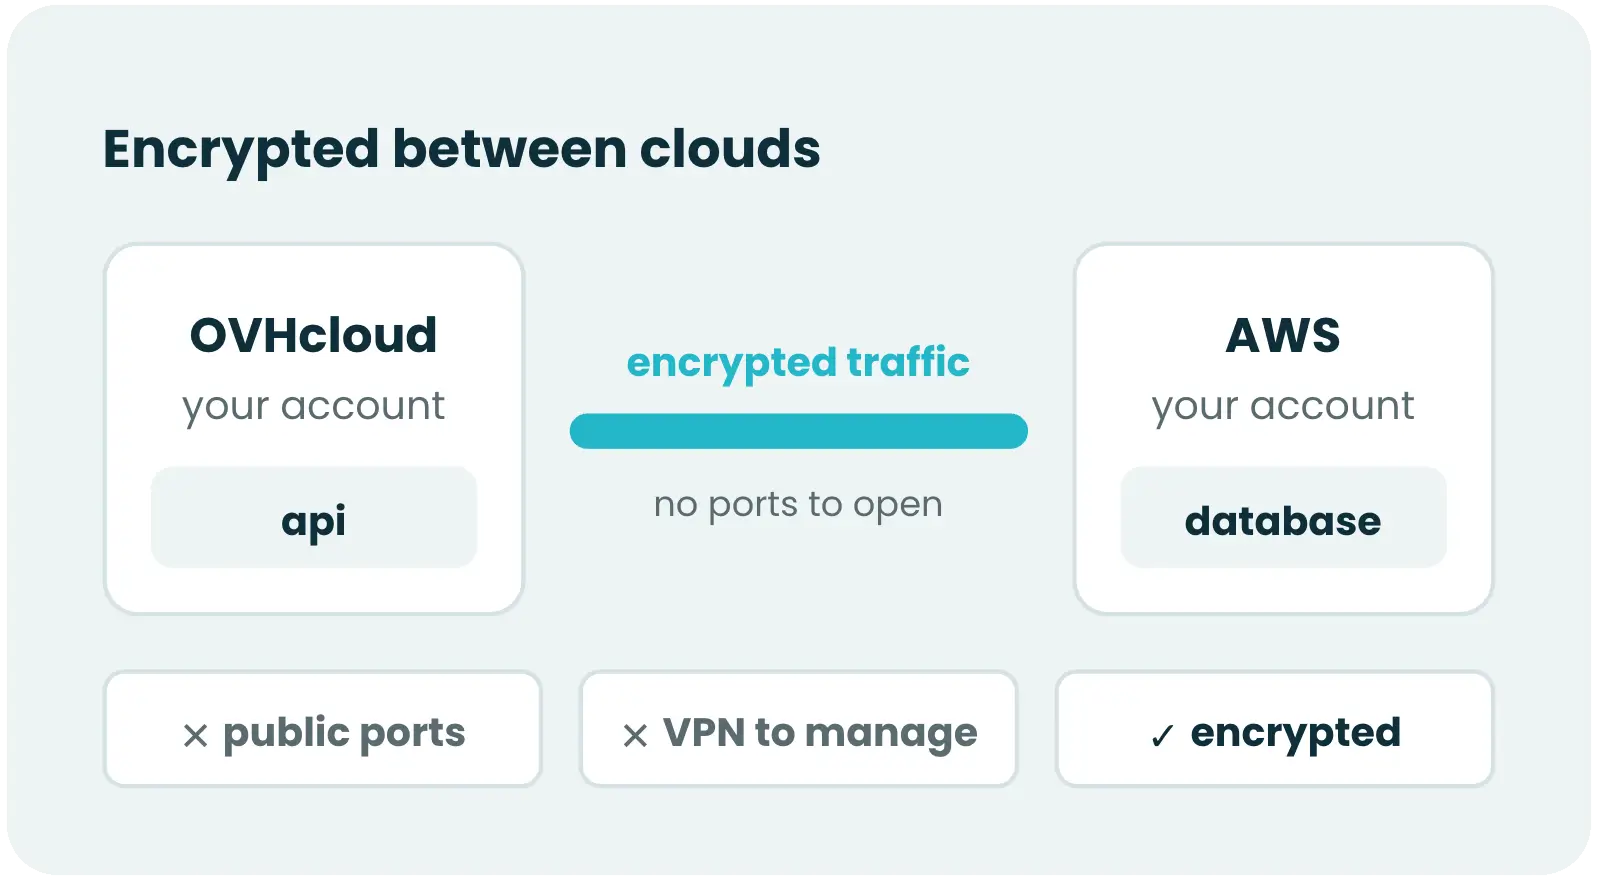
Traffic between services is encrypted, inside the same cloud and between clouds. You do not open a port to the internet, publish an internal service on a public address or set up and maintain a VPN to link accounts. Axebow handles the network; you only see services talking to each other.
One network across every cloud
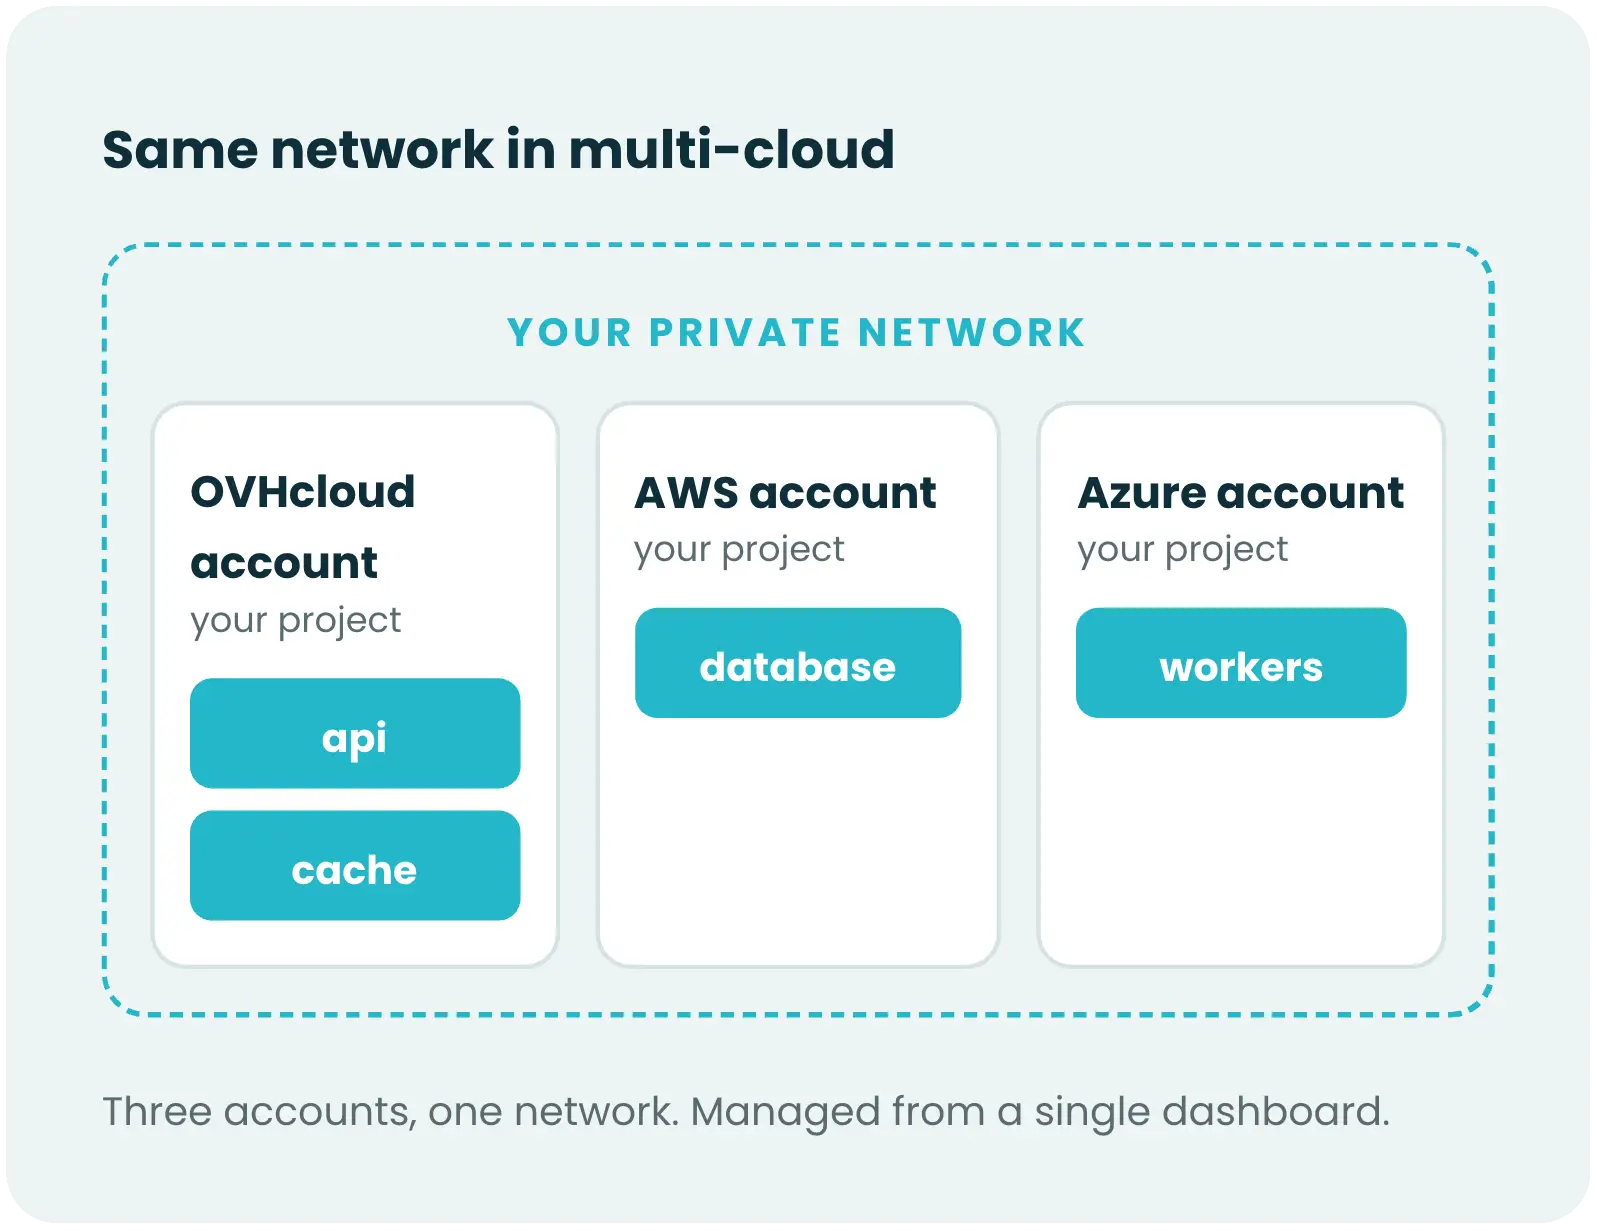
Put the API on OVHcloud, the database on AWS and the workers on Azure. From the point of view of your services, they are all on the same private network. Move a component to another cloud account and the rest keep calling it by the same name, with the same encryption. Split for cost, for credits or for latency, not for what the network allows.
Private network
between services
Every service on one network only your deployment can see.
Encrypted traffic
Inside a cloud and between clouds.
Discovery by name
Services call each other by name, not by IP.
Same network in multi-cloud
OVHcloud, AWS and Azure on one private network.
No public ports exposed
No ports to open, no VPN to set up or maintain.